
China used sophisticated systems to hack into the most secure Operating Software’s to track and spy on its Uighur community movements including here in Malaysia. The recent case of mass hacking on a global scale is extremely alarming, only to shine more light into the Middle Kingdoms alleged dark tactics.
Google had published a blog about vulnerabilities and included Apple users as being exposed to the attacks. Google Project Zero researchers are tasked to look for security flaws on hardware and software across all platform and advice manufacturers accordingly if they find any doors that can be used to form an attack.
Apple has issued a statement regarding Google’s finding and disclaims some of the fact in that report.
“First, the sophisticated attack was narrowly focused, not a broad-based exploit of iPhones “en masse” as described. The attack affected fewer than a dozen websites that focus on content related to the Uighur community. Regardless of the scale of the attack, we take the safety and security of all users extremely seriously.
Google’s post, issued six months after iOS patches were released, creates the false impression of “mass exploitation” to “monitor the private activities of entire populations in real time,” stoking fear among all iPhone users that their devices had been compromised. This was never the case.
Second, all evidence indicates that these website attacks were only operational for a brief period, roughly two months, not “two years” as Google implies. We fixed the vulnerabilities in question in February — working extremely quickly to resolve the issue just 10 days after we learned about it. When Google approached us, we were already in the process of fixing the exploited bugs.
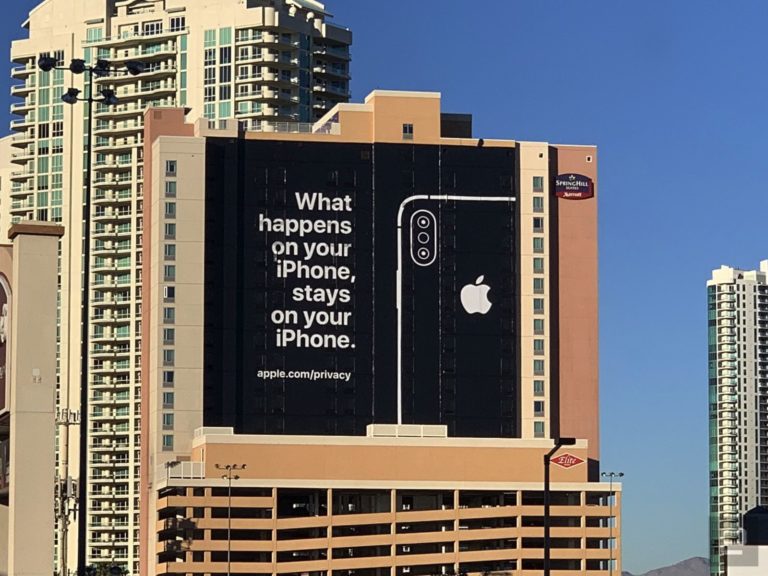
Security is a never-ending journey and our customers can be confident we are working for them. iOS security is unmatched because we take end-to-end responsibility for the security of our hardware and software. Our product security teams around the world are constantly iterating to introduce new protections and patch vulnerabilities as soon as they’re found. We will never stop our tireless work to keep our users safe.”