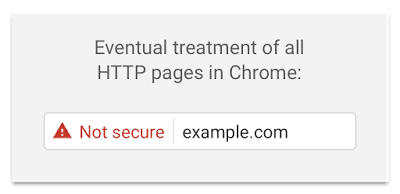


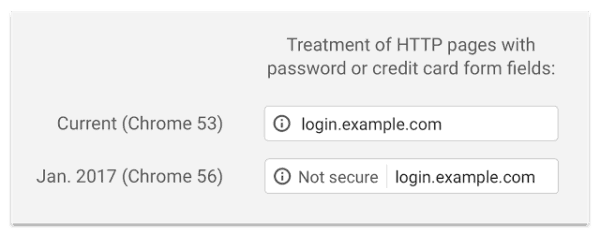
Google Chrome in its security blog update on 8th September 2016 stated that they will have websites under HTTP connections on password prompted and payment pages to alert users on the connections being “non-secure”. Current Chrome 53 does not show the user on which websites are non-secure, so starting from January 2017 on Chrome 56, the user will be alerted on HTTP connections at password prompted and payment pages as being “non-secure”.
After releasing their HTTPS report on February, more and more websites have changed their default landing page to HTTPS rather than HTTP. As a move towards labeling all HTTP connections as non-secure, Google is labeling their password prompted and payment pages as non-secure first. Currently, Google has already make it easier for website owners to switch to HTTPS by giving benefits such as being cheap and better performance.